What production usage looks like
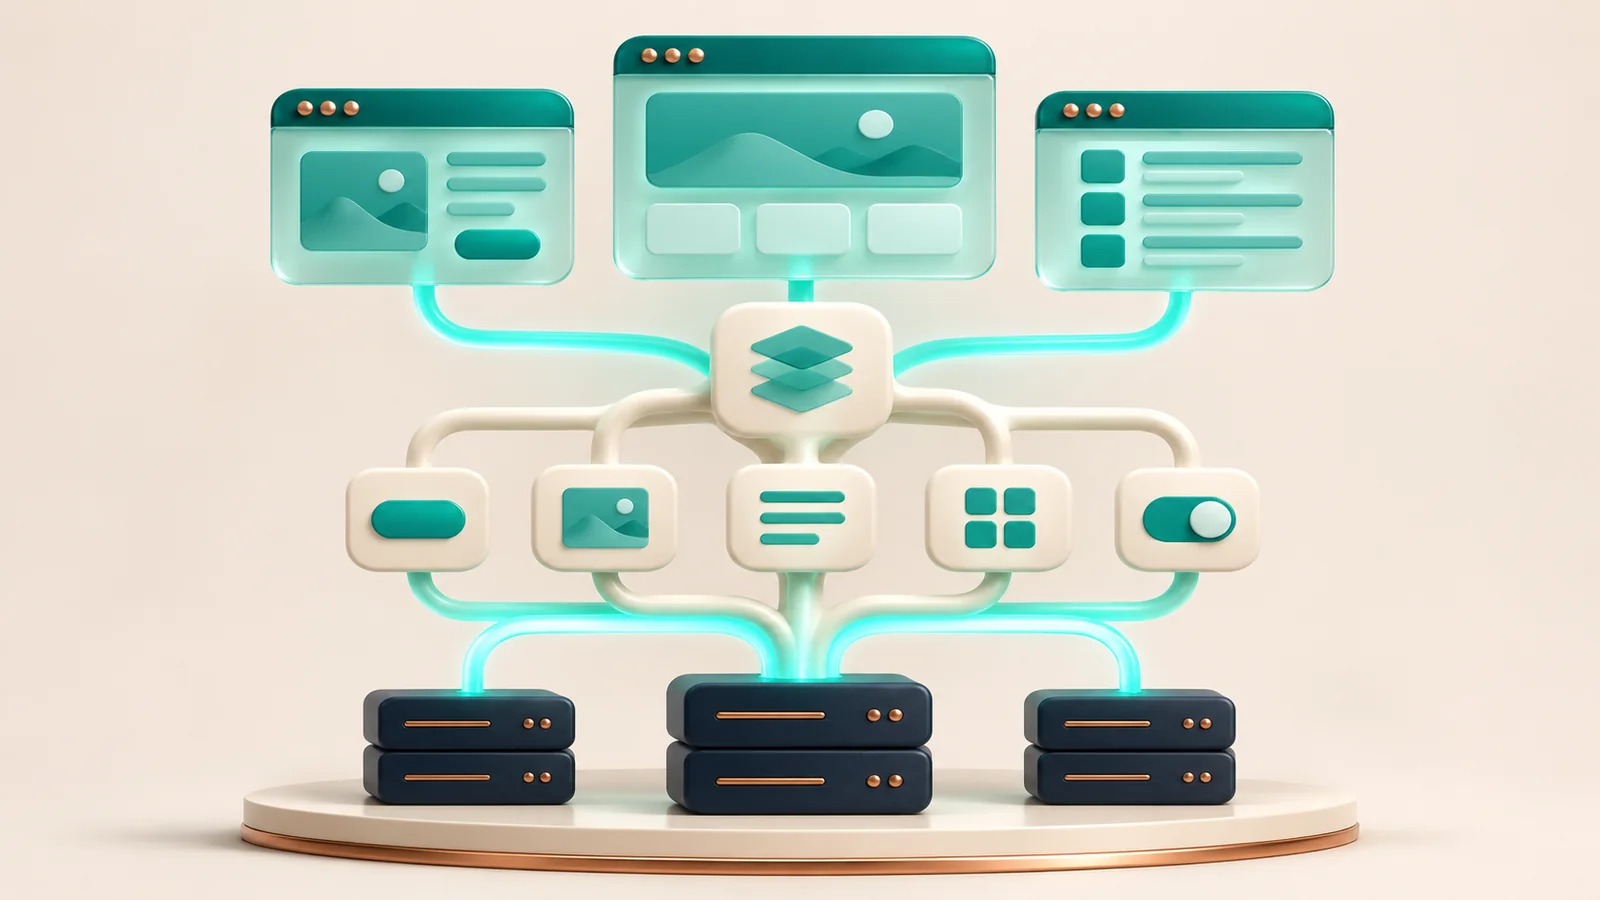
The server-first model quietly changes the default composition of React apps: data fetching and layout live on the server, and client JavaScript is reserved for genuine interactivity. Navigation-heavy pages shrink their bundles without deliberate optimization work.
- Data-heavy screens (dashboards, tables, detail pages) benefit first — markup is streamed with data already attached.
- Input-heavy screens (editors, wizards, canvases) remain client components; resist server-washing them.
- Shared UI stays cleanest as islands: server shells wrapping small client widgets.
A migration that does not stall
The failure mode reported by most teams is converting screens bottom-up, one component at a time, and drowning in boundary errors. The successful pattern inverts it: pick the route tree, make every component server by default, and pull client components out only where the browser genuinely owns state.
Boundaries then become self-documenting: every "use client" marker in the codebase answers why that part of the app genuinely needs the browser.React documentation — Server Components
Further reading
Building a product in this space?
MORE FROM THE NEWSROOM
Related news
 Software Development
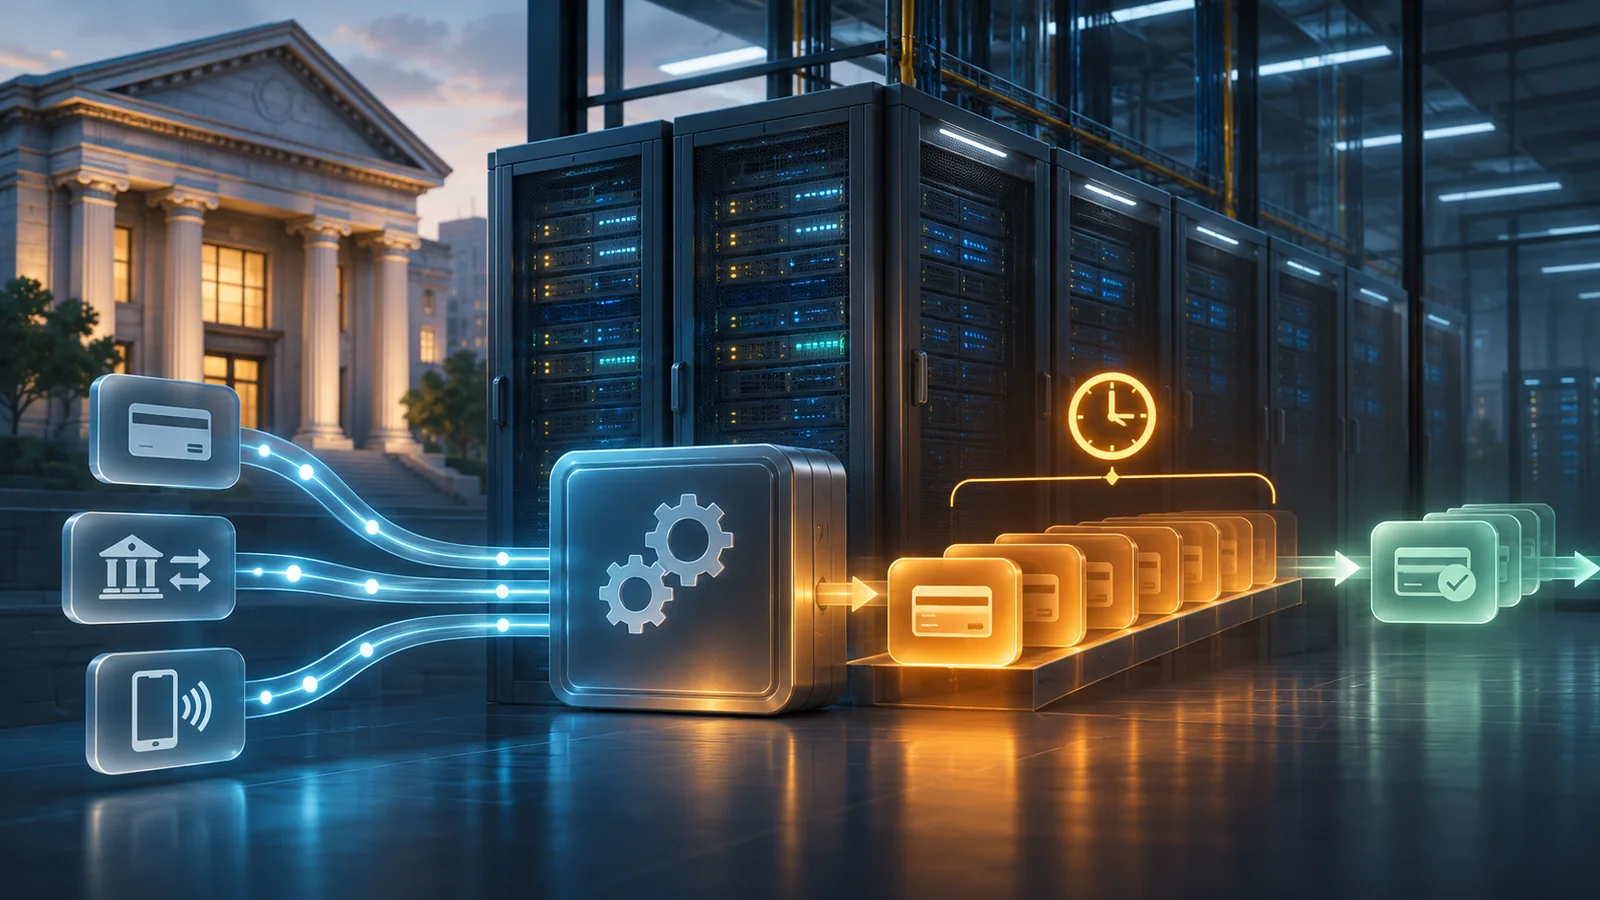
JPMorgan Chase Traces Banking Delays to Software Bug in On-Premise Systems
JPMorgan Chase experienced transaction-processing delays on 16 November after a software bug affected its on-premise hardware systems. The bank said customers retained access to their accounts and funds, while some transactions involving other financial institutions could also experience delays.
 Software Development
Microsoft Releases .NET 11 With C# 15, Faster Developer Tools and New AI Development Capabilities
Microsoft has officially released .NET 11, introducing C# 15, runtime optimizations, improved SDK tooling and additional capabilities for AI-powered application development. The release also brings new MCP server templates and deeper integration with Microsoft's agent development ecosystem, making it an important update for backend developers and enterprise engineering teams.
 Cybersecurity
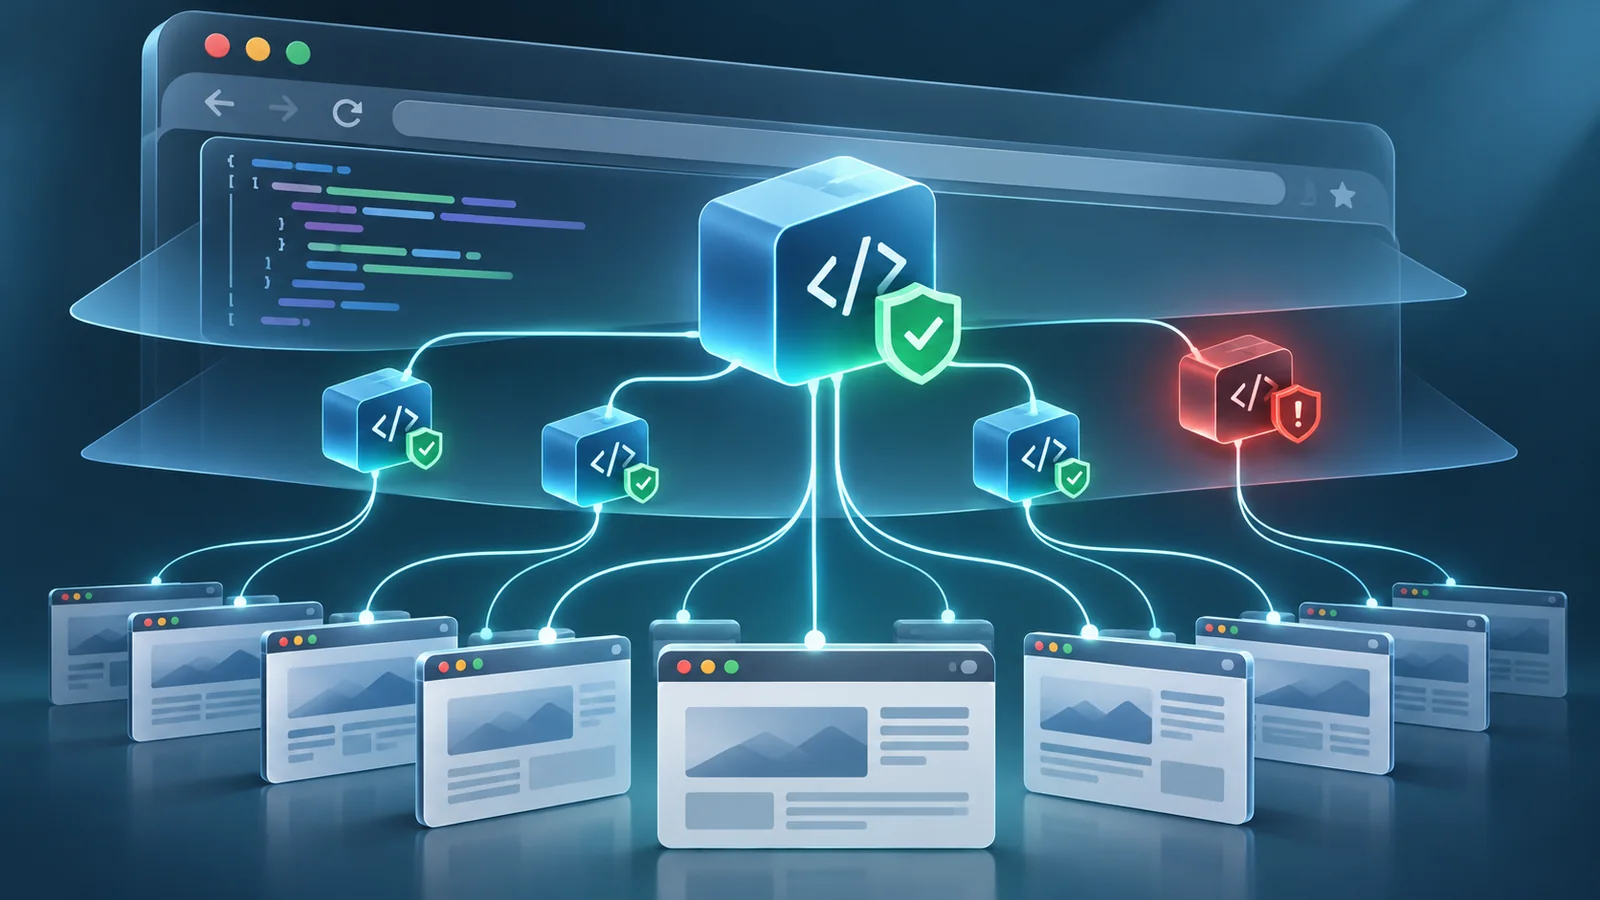
Malicious Optimizely Scripts Reached 178 Organizations, Exposing Website Visitors to Data Theft
A malicious JavaScript campaign distributed through Optimizely Web reached visitors across 178 organizations, according to security researcher Scott Helme. The payload included cryptocurrency address substitution, payment-card skimming, cookie theft and iOS exploit delivery mechanisms, highlighting the security risks associated with trusted third-party website scripts.