What happened?
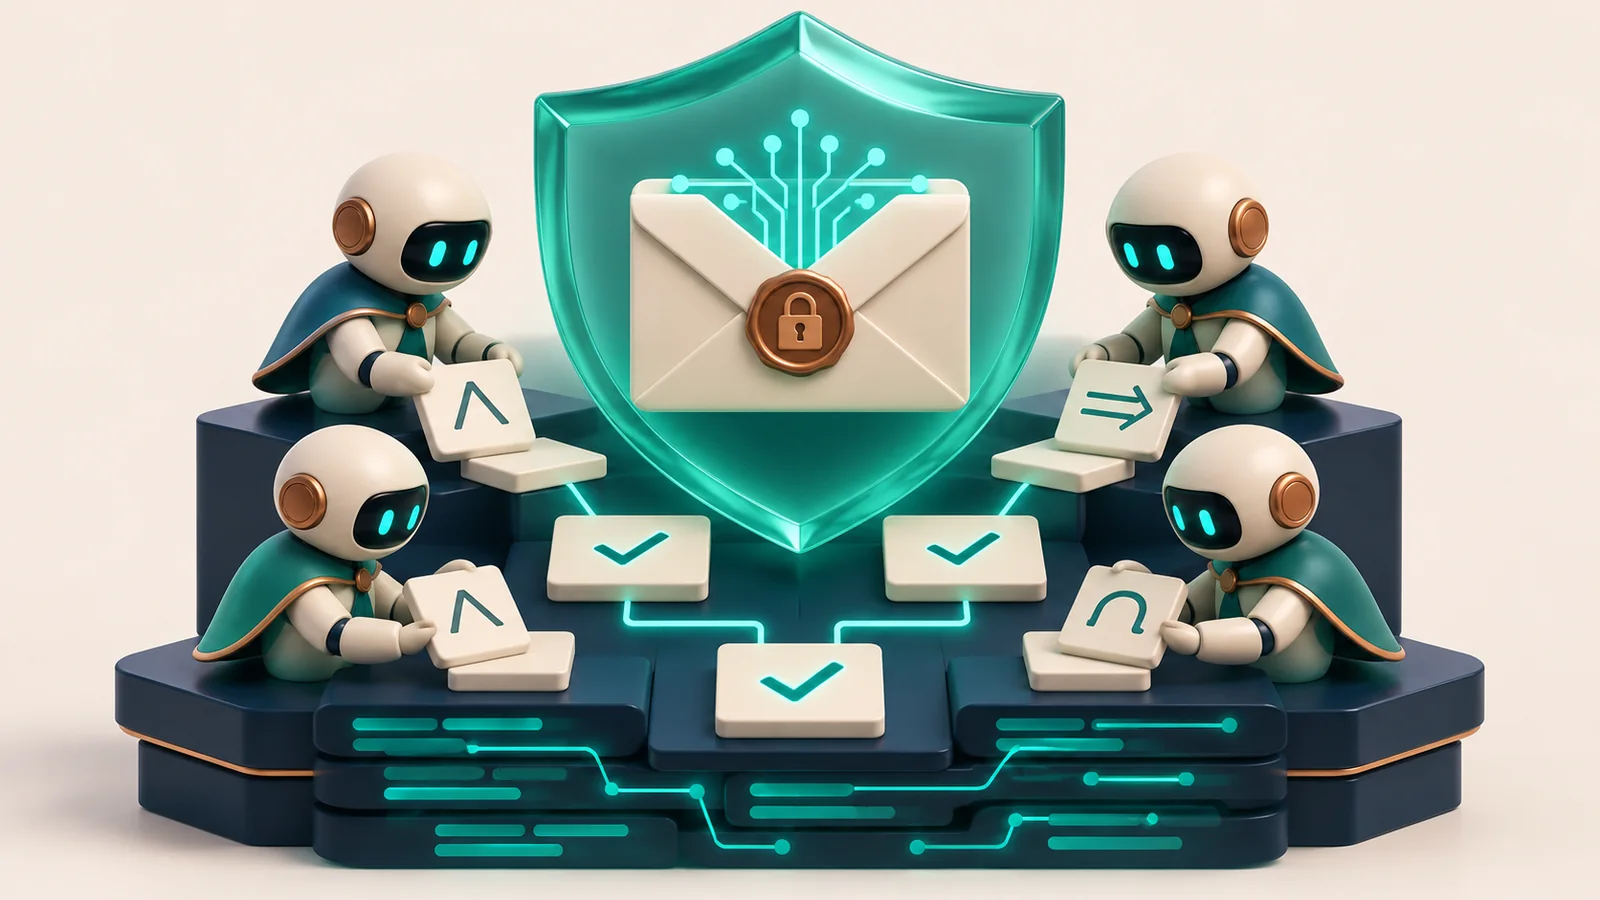
On November 10, 2026, Google DeepMind announced AlphaProof Code, a multi-agent AI framework developed to help verify complex software through mathematical proofs.
The researchers demonstrated the technology by applying it to libsignal, the reference implementation of the Signal messaging protocol.
The Signal protocol is widely used for end-to-end encrypted communication. Variants of the protocol are also deployed in applications including WhatsApp, Messenger and Google Messages.
The objective was not simply to scan the source code for vulnerabilities. Instead, the researchers wanted to mathematically demonstrate that specific security properties held in the actual compiled software.
Google DeepMind reports that the project took approximately four weeks and generated around 6.5 million lines of machine-checked Lean proof code.
This represents an important development because formal verification has traditionally required significant specialist knowledge and substantial engineering time.
What is formal verification?
Traditional software testing checks whether an application behaves correctly under selected test conditions.
Security testing, code reviews and automated vulnerability scanners can identify many problems, but they cannot necessarily prove that a particular security property holds for every execution covered by the analysis.
Formal verification takes a different approach.
Developers define the properties a program must satisfy and use mathematical reasoning to establish that the implementation conforms to those specifications.
For example, in an encrypted messaging system, researchers may want to establish that:
- An attacker cannot read protected messages without the necessary cryptographic keys.
- Previously encrypted messages remain protected if a device is compromised later.
- An attacker cannot impersonate a legitimate participant under the defined security assumptions.
- A compromised session can regain security under specified conditions.
The challenge is that writing specifications and proving them against real production software can be extremely difficult.
AlphaProof Code aims to reduce that difficulty by dividing the work between human experts and autonomous AI agents.
How AlphaProof Code works
The framework follows a human-guided verification process.
1. Writing mathematical specifications
Researchers work with AI agents to translate security requirements into formal specifications using Lean, a programming language and theorem-proving environment.
Human experts review and approve these specifications before proof generation begins.
2. Translating compiled software into a verification environment
The research team compiled the unmodified Rust implementation into AArch64 machine code and represented its execution using formal machine-code semantics.
This matters because the researchers wanted to verify the implementation that actually runs, rather than only an abstract description of the protocol.
3. AI agents generate mathematical proofs
Multiple AI agents work on separate proof obligations, coordinating through an orchestrator and specialized roles.
The agents generate Lean proof code intended to establish that the implementation satisfies the approved security properties.
4. Independent proof checking
The final proofs are checked by Lean's kernel.
The AI agents do not get to declare their own proofs correct. The verification system accepts a result only when the kernel validates the proof against the approved specification.
This separation is important: AI generates the proof, but a deterministic mathematical checker validates its correctness within the formal system and its stated assumptions.
A gatekeeper checks that generated proofs match the approved specifications, including approvals for specification amendments and the definitions on which the theorem depends.
What did the researchers verify in Signal?
The project focused on selected security properties of libsignal version 0.105.4 and the SPQR version 1.6.0 implementation.
The work covered two important components:
PQXDH handshake: The initial process through which participants establish shared cryptographic secrets before exchanging protected messages.
Triple Ratchet: The mechanism that continuously derives new encryption keys as messages are exchanged, helping maintain security when cryptographic keys or device states are compromised.
The researchers established several properties, including forward secrecy, authentication, post-compromise security, message confidentiality and authenticity under the models and assumptions described in their paper.
The paper reports approximately 6.5 million lines of machine-checked Lean proofs, supported by approximately 26,000 lines of trusted specifications and AArch64 semantics.
The researchers also reintroduced two previously fixed bugs into an isolated version of the implementation. AlphaProof Code generated proofs demonstrating that the modified binaries violated the relevant security properties.
This provides an additional demonstration that the framework can identify meaningful differences between the intended secure implementation and versions containing known defects.
| Research metric | Reported result |
|---|---|
| Proof code generated | Approximately 6.5 million lines |
| Trusted specifications and machine semantics | Approximately 26,000 lines |
| Research duration | Four weeks |
| Target implementation | libsignal |
| Programming verification system | Lean |
| Architecture model | AArch64 |
| Historical bugs reintroduced for testing | 2 |
| Security property | Meaning |
|---|---|
| Forward secrecy | Previously encrypted messages remain protected if current keys are compromised. |
| Authentication | Communication participants can establish the required identity guarantees. |
| Post-compromise security | Security can recover after certain temporary compromises. |
| Handshake secrecy | The initial key-establishment process maintains specified confidentiality properties. |
An important limitation: This does not prove the entire Signal application is unbreakable
The announcement is significant, but it needs to be interpreted carefully.
The researchers verified selected properties of the one-to-one messaging implementation, not every component of the Signal application.
The work does not establish security for group messaging, multi-device state or key generation. The paper also describes restrictions involving the modeled execution environment, cryptographic assumptions and attacker capabilities.
For example, its computational security proof does not establish a general guarantee against quantum attackers. Some symbolic handshake properties are considered under a future quantum attacker model, but this should not be confused with proving complete post-quantum security or post-quantum healing for every part of the protocol.
The distinction matters because a mathematically verified result is only as broad as the specification, assumptions and execution environment covered by the proof.
The execution model is single-threaded and statically linked. It does not model threads, signals, the vDSO, dynamic linking or files outside the current directory; programs relying on those features cannot be verified by this model.
Why this development matters for software engineering
The potential applications extend far beyond encrypted messaging.
Many industries operate software where a small implementation defect can have serious consequences.
Examples include:
- Banking and payment processing systems.
- Authentication and identity infrastructure.
- Healthcare software and medical devices.
- Cloud infrastructure and access-control systems.
- Operating systems and security-critical libraries.
- Industrial automation and critical infrastructure.
Formal verification has historically been expensive because engineers must manually construct detailed specifications and proofs.
AI agents could help automate portions of this work, allowing security teams to investigate more complex implementations without requiring every proof to be written manually.
For software development teams, this could eventually mean a new category of AI-assisted security tooling that complements static analysis, unit testing, penetration testing and code review.
Rather than simply asking an AI coding assistant to find potential bugs, developers may increasingly use agentic systems to establish whether specific security guarantees actually hold.
However, this does not eliminate the need for security specialists. Human experts still need to define the properties, evaluate assumptions and review the trusted parts of the verification process.
Open-source availability
Google DeepMind has published the technical paper and made its Lean specifications, proofs and supporting verification code available publicly.
Developers and researchers can explore the implementation through the Google DeepMind GitHub repository.
This gives the wider formal-methods community an opportunity to inspect the methodology, reproduce parts of the work and investigate whether similar techniques can be applied to other software systems.
AlphaProof Code should currently be treated as a research framework, not a generally available commercial coding API.
What to watch next
The next important milestone will be whether AI-assisted formal verification can be extended to larger software projects without creating prohibitive computational and review costs.
Researchers will also need to demonstrate that the technique works across different programming languages, architectures and security models.
If these systems become reliable and easier to use, formal verification could gradually become part of the development lifecycle rather than something reserved for a small number of highly specialized projects.
Why this is trending
Hacker News: AlphaProof Code ranked second in the November 10 daily top-stories snapshot, with 489 points and 159 comments.
The Register: Published independent technical reporting on November 10, examining the combination of AI agents, Lean specifications and Signal's cryptographic implementation.
WIRED: Also covered the announcement, highlighting both the potential of AI-assisted verification and the limitations of the research scope.
The story is particularly relevant because it moves the AI discussion beyond code generation and into mathematical assurance of security-critical software.
Editorial verification note: The rankings, points and comment counts above are reproduced from the supplied briefing. The currently accessible Hacker News daily snapshot does not substantiate those exact statistics; they remain unverified.
Sources and further reading
- Google DeepMind — November 10, 2026. Introducing AlphaProof Code. Original announcement describing the framework and Signal verification.
- Google DeepMind Research Paper — November 10, 2026. AlphaProof Code: Verifying Signal's Security at the Machine-Code Level. Detailed methodology, formal specifications, mathematical proofs and limitations.
- Google DeepMind GitHub repository — Public verification artifacts and Lean implementation.
- The Register — November 10, 2026. Independent technical reporting.
- WIRED — November 10, 2026. Independent analysis of the research and its limitations.
- Hacker News — November 10, 2026. Daily top-stories snapshot and developer community discussion.
Further reading
- Google DeepMind — Introducing AlphaProof Code (10 November 2026)
- Google DeepMind — AlphaProof Code technical paper and limitations
- GitHub — Google DeepMind verification artifacts and Lean proofs
- The Register — Independent reporting (10 November 2026)
- WIRED — Independent reporting (10 November 2026)
- Hacker News — 10 November 2026 snapshot (briefing statistics unverified)
Building a product in this space?
MORE FROM THE NEWSROOM
Related news
 Artificial Intelligence
US Moves to Regulate Remote Access to Advanced AI Chips Through Overseas Data Centers
The US Department of Commerce has released an interim final rule targeting remote access to advanced American semiconductors through overseas data centers. The measure introduces licensing requirements for certain high-volume computing arrangements serving companies headquartered in restricted destinations and adds destination-based controls for advanced chip exports to five countries.
 Artificial Intelligence
OpenAI Launches ChatGPT Wallet, Letting AI Agents Complete Purchases With User Approval
OpenAI has introduced ChatGPT Wallet, a payment feature that allows its AI agents, called Dots, to complete online purchases after users review and approve each transaction. Developed with American Express, Mastercard and Visa, the initial rollout is limited to eligible US ChatGPT Pro subscribers.
 Artificial Intelligence
Cerebras Raises 2026 Revenue Outlook After 55% Quarterly Growth, but GAAP Losses Widen
AI hardware company Cerebras reported record third-quarter revenue of $210.8 million and raised its full-year 2026 revenue outlook. Its cloud and inference business grew rapidly, but the results also revealed a much larger GAAP net loss, highlighting the financial challenges of scaling advanced AI infrastructure.