Overview
A new software supply-chain security incident is highlighting how compromised developer accounts can become an entry point into production infrastructure.
Security researchers from Aikido Security and StepSecurity have documented a campaign known as WFX-Loot, in which attackers used stolen GitHub credentials to access repositories, introduce malicious CI/CD changes and extract sensitive credentials from automated build environments.
Aikido's investigation, published on 12 November 2026, reports that 4,837 compromised accounts opened probe pull requests across 61,764 repositories. The researchers identified evidence that the malicious payload executed in more than 1,800 repositories. The Hacker News reported Aikido's more conservative detailed figure of at least 1,806 affected repositories, while Aikido's summary also gives a figure of 1,835. These are researcher-reported estimates, not a verified GitHub-wide incident count.
The incident is particularly concerning because the attackers did not need to exploit a new vulnerability in GitHub Actions. Instead, they abused legitimate access credentials belonging to developers and automated accounts.
How the attack works
The campaign began on 10 November 2026, according to Aikido.
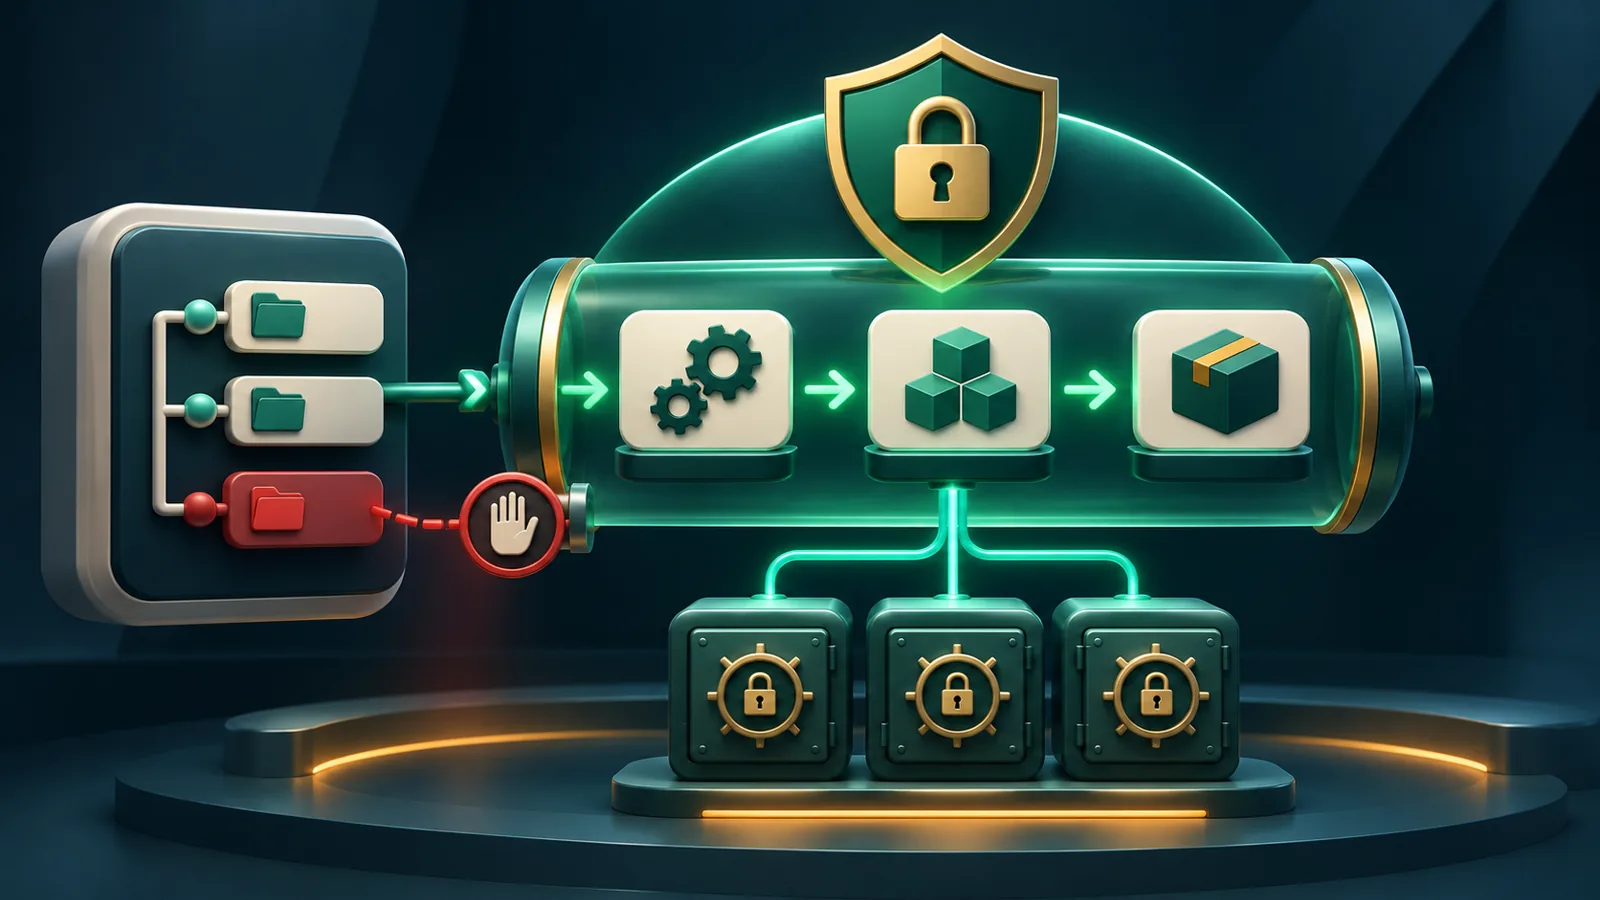
Researchers describe a three-stage process.
1. Testing repository access
The attackers used compromised GitHub credentials to open seemingly harmless pull requests with the title:
docs: dependency audit notes
The requests originated from branches named wfx-docs. Their purpose was to establish whether the compromised account had write access to a repository.
Aikido counted 61,764 repositories receiving these probes. Importantly, this number represents repositories tested for access, not repositories where the malicious payload successfully executed.
2. Introducing the credential stealer
Where permissions and repository configurations allowed it, the attackers introduced a malicious shell script of approximately 1,500 lines.
Researchers identified several delivery methods:
- Adding malicious steps to an existing GitHub Actions workflow.
- Creating a hidden
.ci-*.shscript and connecting it to an npmpostinstallhook. - Adding a new workflow file on a temporary branch.
- Inserting malicious code into an existing shell script that a workflow already executes.
The changes were disguised using commit messages such as ci: refresh build cache and chore: add ci helper.
3. Removing evidence
After the payload executed, the attacker attempted to reverse the malicious changes and delete workflow runs and logs.
This created a serious forensic problem. A repository might no longer contain the malicious file, while the credentials accessible to its workflow had already been extracted.
StepSecurity specifically recommends checking for missing run numbers in GitHub Actions history following suspicious commits.
What information did the payload collect?
The malicious script was designed to collect information available to the compromised workflow runner.
Researchers identified the following categories:
| Data category | Potentially exposed information |
|---|---|
| GitHub credentials | Actions secrets, variables, GITHUB_TOKEN, OIDC tokens |
| Cloud credentials | AWS, Azure and Google Cloud access credentials |
| AI services | API keys for OpenAI, Anthropic, Gemini and developer AI tools |
| Developer infrastructure | Docker, Kubernetes, npm, PyPI, SSH and Vault credentials |
| Runner environment | Process memory, environment variables and shell histories |
| Repository information | Source code, recent commits and workflow artifacts |
The inclusion of AI-service credentials is particularly important for companies running AI-assisted development pipelines. A compromised build runner could expose keys used for model APIs, coding assistants and other automated services.
Why rotating passwords and API keys may not be enough
One of the most serious elements of the campaign is its reported persistence mechanism.
Aikido and StepSecurity describe techniques designed to maintain cloud access even after organizations rotate their original credentials.
Examples include:
- Creating long-lived AWS access keys.
- Changing AWS role trust policies to permit broader access.
- Adding Azure federated identity credentials with names beginning
wfx-ci-. - Reusing GitHub OIDC authentication to obtain cloud sessions.
These techniques mean that simply deleting a malicious workflow and rotating a few API keys may not fully resolve an incident. The associated cloud identity configuration must also be investigated.
StepSecurity also identified a change in the attacker's data-exfiltration approach on 12 November. Later samples used Telegram as the destination for stolen information, reducing the effectiveness of relying only on previously published malicious IP addresses.
What developers and businesses should do
Organizations using GitHub Actions should treat this as an identity and infrastructure-security problem, not simply a malware-removal exercise.
Recommended response:
- Search repositories for
wfx-docsbranches and pull requests titleddocs: dependency audit notes. - Investigate commits titled
ci: refresh build cache,chore: add ci helperandchore: add dependency audit workflow. - Examine GitHub Actions history for missing or deleted workflow runs.
- Revoke suspicious personal access tokens, OAuth grants, SSH keys and active sessions.
- Rotate every credential that an affected workflow could access.
- Review AWS CloudTrail, Azure Entra ID and Google Cloud identity logs for unauthorized access and persistence.
- Restrict CI/CD permissions to the minimum required for each workflow.
- Use network egress controls and separate privileged deployment workflows from ordinary pull-request workflows.
For teams maintaining production SaaS applications, a particularly useful improvement is to prevent untrusted pull-request code from accessing deployment secrets or production cloud identities.
What remains unknown?
The researchers have not established exactly how the original GitHub credentials were obtained. StepSecurity also identified some probe pull requests associated with tokens issued through the Fly.io GitHub App, but explicitly said it had no evidence of a breach of Fly.io's own infrastructure.
The number of affected private repositories is also uncertain because public GitHub searches cannot reveal the complete activity across private environments.
The researchers' figures come from different collection windows and methodologies. They should not be added together or interpreted as a single confirmed victim count.
What to watch next
The next important developments will be additional incident-response findings, possible GitHub security guidance and evidence of further cloud-account compromise.
The larger lesson for engineering organizations is that the security of a source-code repository is closely connected to the security of its automation infrastructure. A stolen developer token can be much more damaging when it also grants access to build pipelines, deployment systems and cloud credentials.
Why this is trending
- daily.dev: Its Highlights page listed the WFX-Loot investigation among recent developer-security stories, approximately 14 hours before retrieval.
- Hacker News: No matching WFX-Loot story was found on the 13 November front page.
- TechCrunch: No matching report was found in the retrieved technology and AI feeds.
- Reddit: Searches did not return a useful current discussion about this specific campaign. Older, unrelated GitHub incidents were excluded.
- X: Direct search access was unavailable, so current engagement could not be verified.
- Independent security reporting: The Hacker News and Help Net Security published separate reports based on the research, while Aikido and StepSecurity supplied distinct technical analyses.
The strongest verified signals are the developer-news appearance and the independent technical investigations. No unsupported cross-platform popularity claim is made.
Sources
- Aikido Security — wfx-loot campaign pushes CI secret stealer to tens of thousands of repositories — 12 November 2026. Primary technical research, affected-account estimates, payload behavior and indicators of compromise.
- StepSecurity — WFX Phantom: The GitHub Actions Secret Stealer That Deletes Its Tracks — 12 November 2026. Independent technical analysis of the delivery methods, Telegram exfiltration and persistence mechanisms.
- The Hacker News — Attacker Used 4,837 Hijacked GitHub Accounts to Run a CI Secret Stealer in 1,806+ Repositories — 12 November 2026. Cross-checks the attack scale, SafeDep findings and defensive indicators.
- Help Net Security — Check your GitHub repos: A secret stealer hit tens of thousands of them — 12 November 2026. Independent cybersecurity reporting and response guidance.
- SafeDep — wfx: GitHub Actions Credential Stealer Hits 8,000 Repos — 12 November 2026. Additional public-repository analysis; its count measures repositories with malicious commits, not only confirmed successful exfiltration.
Further reading
- Aikido Security — wfx-loot campaign pushes CI secret stealer to tens of thousands of repositories — 12 November 2026. Primary technical research, affected-account estimates, payload behavior and indicators of compromise.
- StepSecurity — WFX Phantom: The GitHub Actions Secret Stealer That Deletes Its Tracks — 12 November 2026. Independent technical analysis of the delivery methods, Telegram exfiltration and persistence mechanisms.
- The Hacker News — Attacker Used 4,837 Hijacked GitHub Accounts to Run a CI Secret Stealer in 1,806+ Repositories — 12 November 2026. Cross-checks the attack scale, SafeDep findings and defensive indicators.
- Help Net Security — Check your GitHub repos: A secret stealer hit tens of thousands of them — 12 November 2026. Independent cybersecurity reporting and response guidance.
- SafeDep — wfx: GitHub Actions Credential Stealer Hits 8,000 Repos — 12 November 2026. Additional public-repository analysis; its count measures repositories with malicious commits, not only confirmed successful exfiltration.
Building a product in this space?
MORE FROM THE NEWSROOM
Related news
 Cybersecurity
Malicious Optimizely Scripts Reached 178 Organizations, Exposing Website Visitors to Data Theft
A malicious JavaScript campaign distributed through Optimizely Web reached visitors across 178 organizations, according to security researcher Scott Helme. The payload included cryptocurrency address substitution, payment-card skimming, cookie theft and iOS exploit delivery mechanisms, highlighting the security risks associated with trusted third-party website scripts.
 Cybersecurity
Uber Driver Information Exposed After Fireworks AI Vendor Breach, State Filings Reveal
Uber has confirmed that personal information belonging to drivers was accessed through compromised credentials at a third-party technology provider identified as Fireworks AI. Public breach notices and independent reporting identify at least 7,870 affected individuals across Massachusetts, South Carolina and Rhode Island, with additional state notifications still being assessed.
 Cybersecurity
SignDrop Windows Zero-Day Exposes Local SYSTEM Privilege-Escalation Path; Microsoft Investigates
Security researcher Abdelhamid Naceri has disclosed SignDrop, a Windows privilege-escalation vulnerability involving the Common Log File System and Microsoft Defender. A public proof of concept demonstrates a path from an existing local user account to SYSTEM privileges, although Microsoft says Defender detects and blocks the associated exploit behavior and that it has not observed exploitation in the wild.